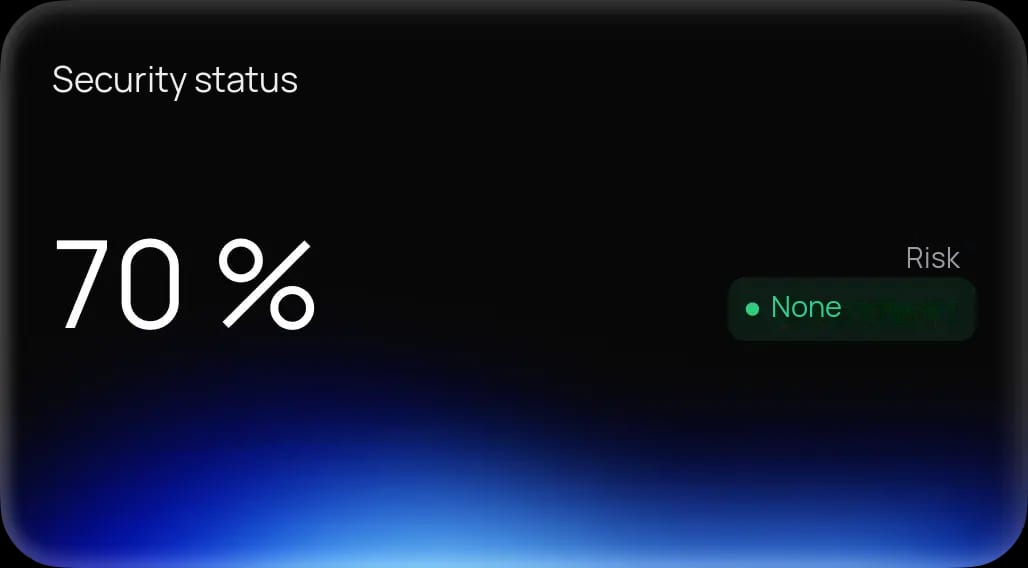
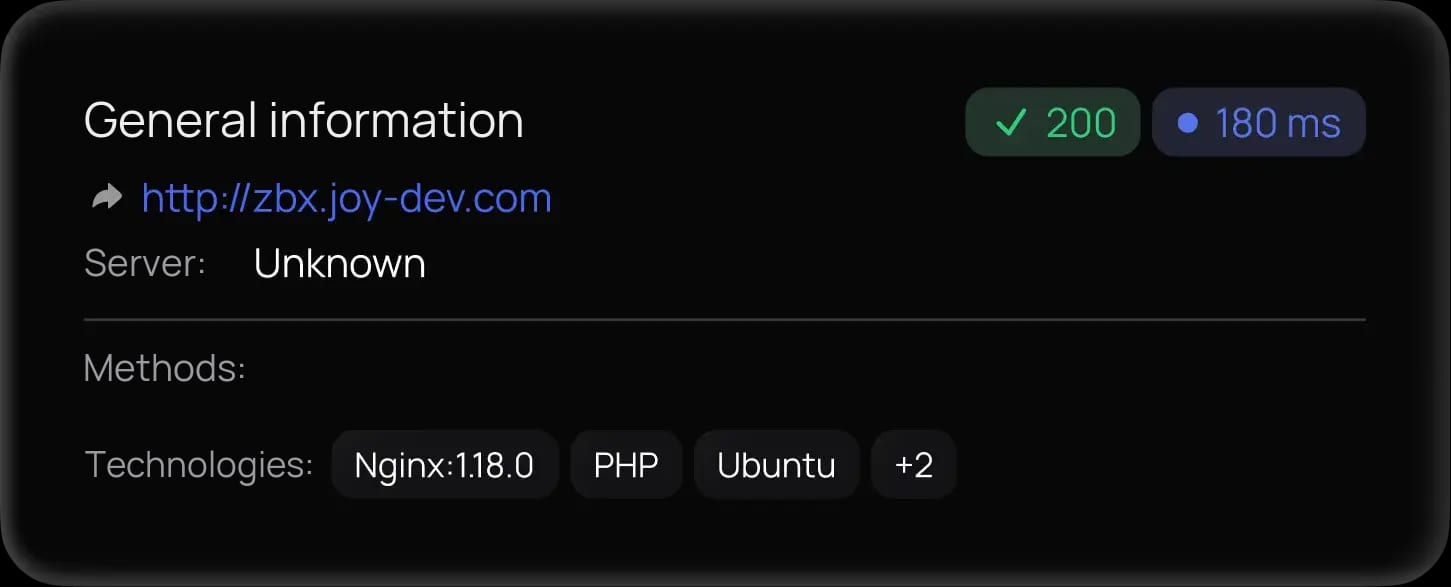
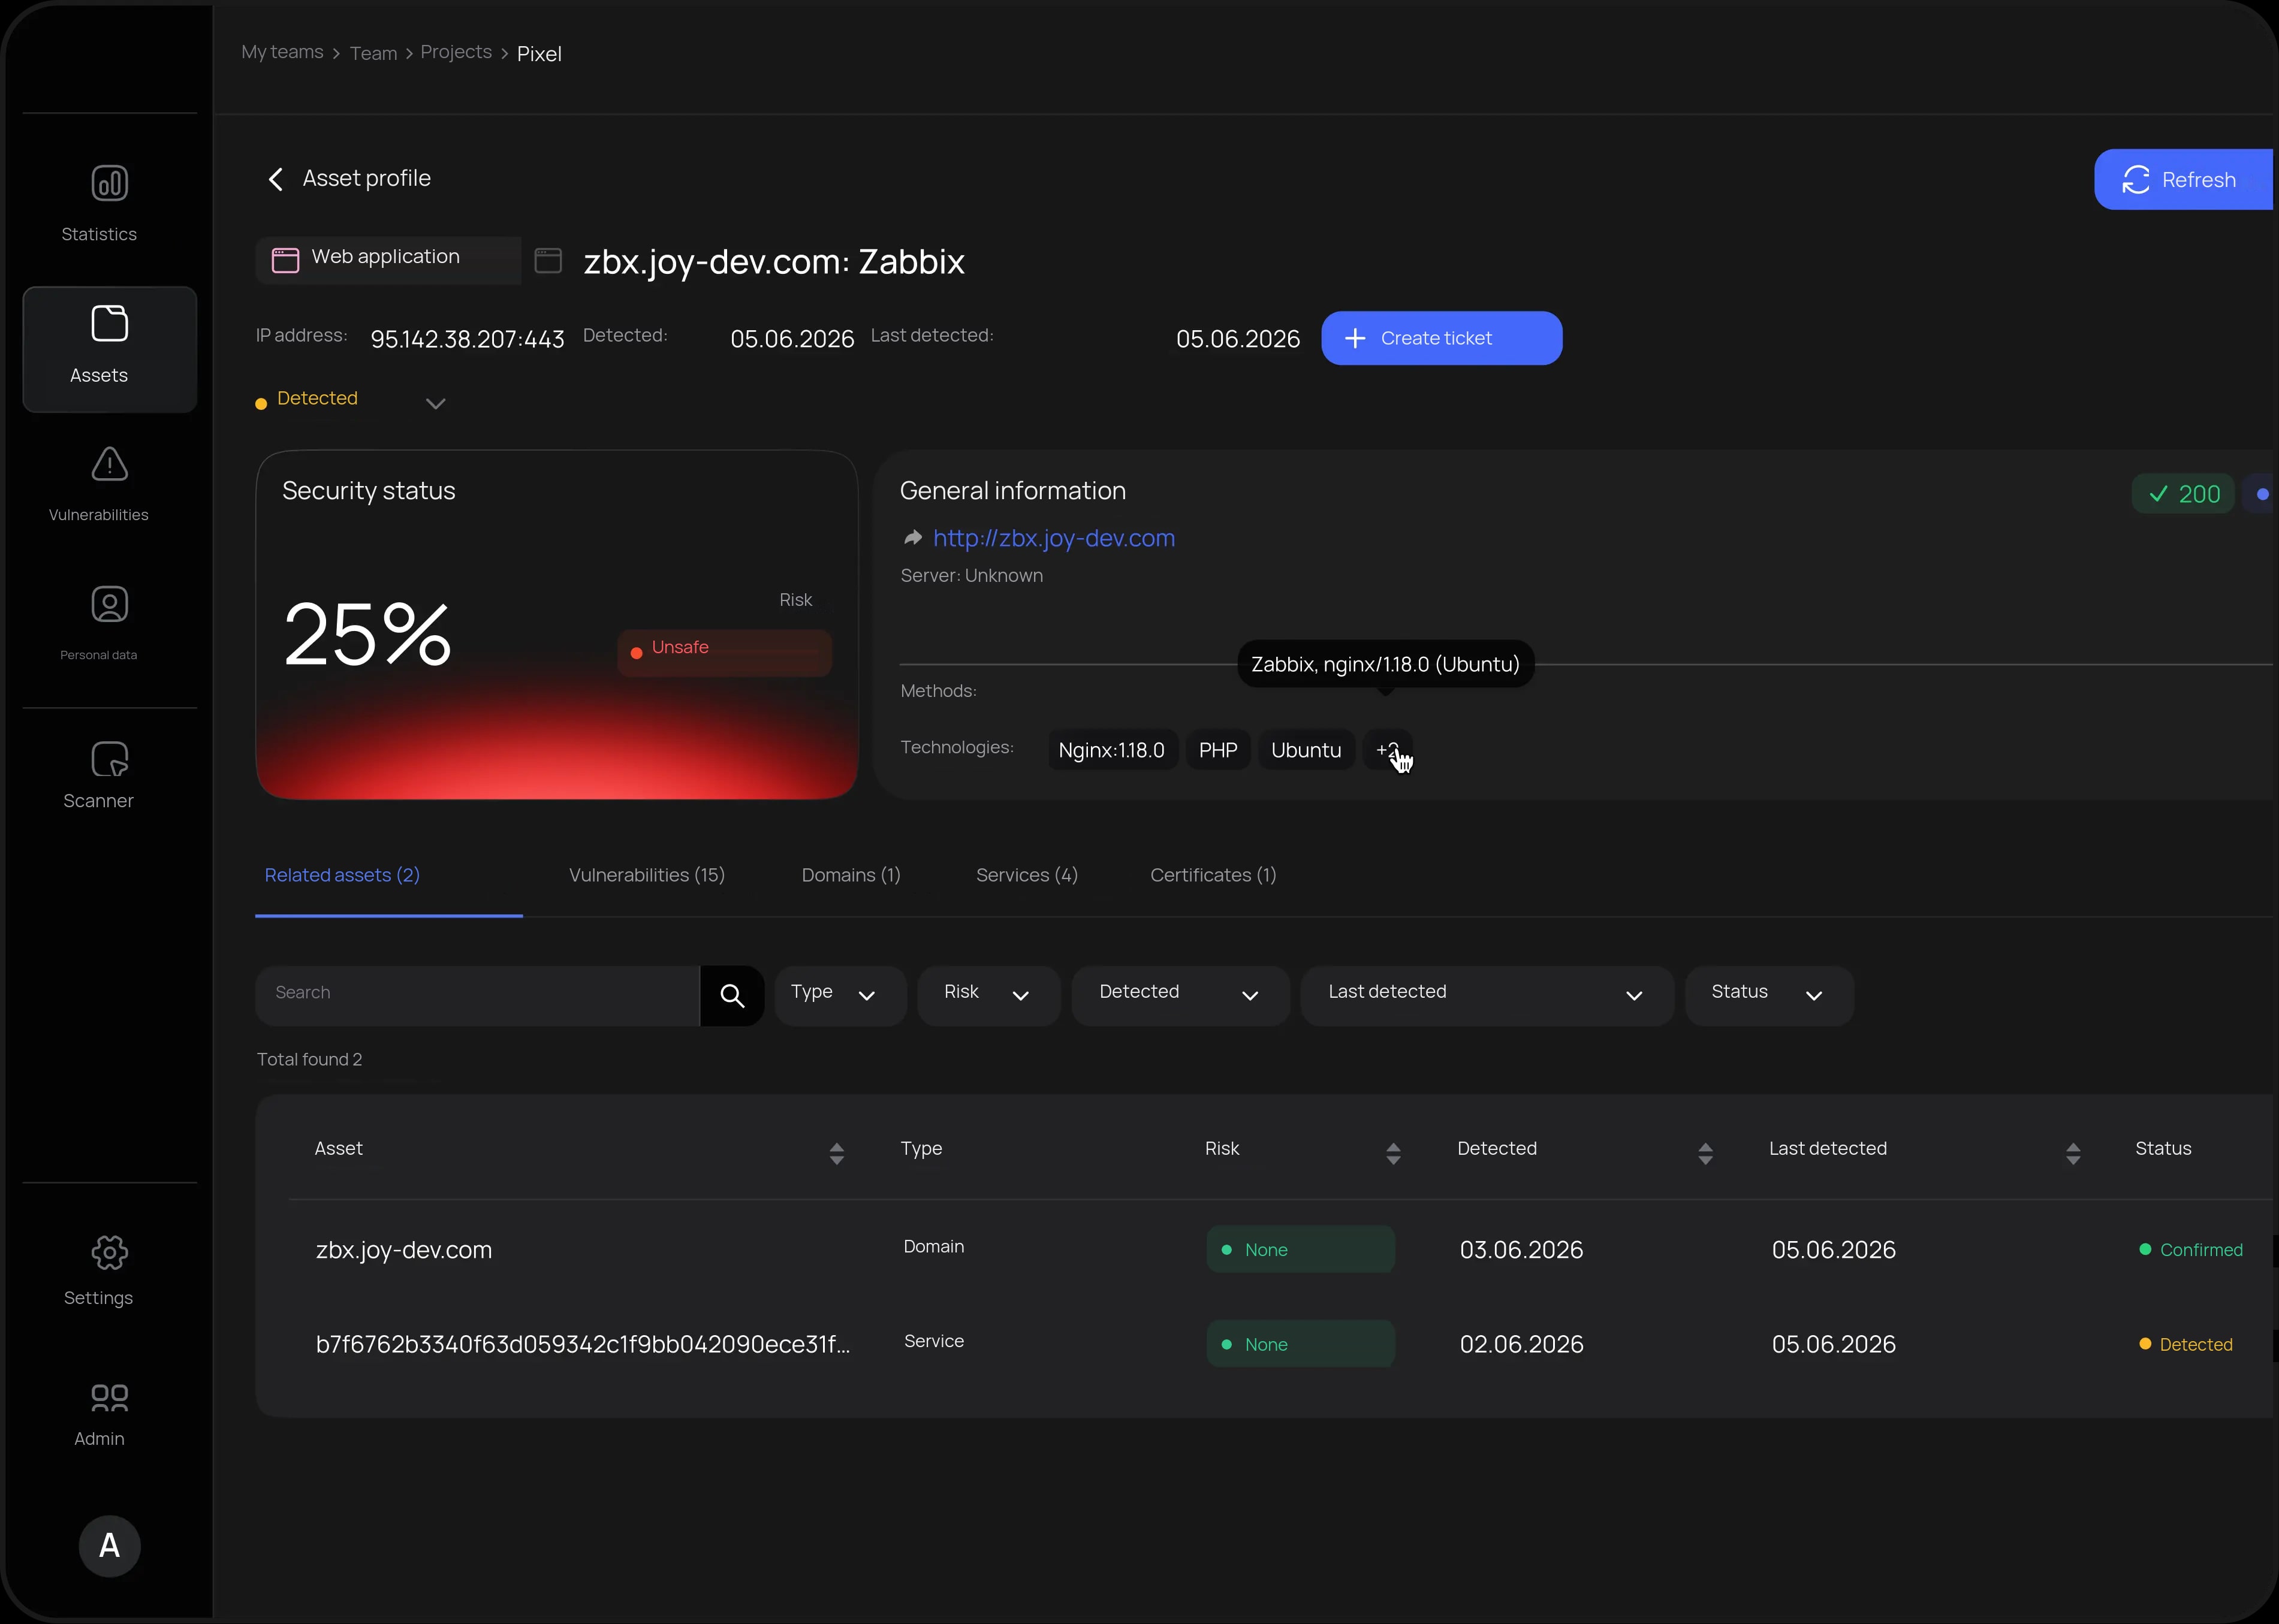
Shadow IT asset discovery
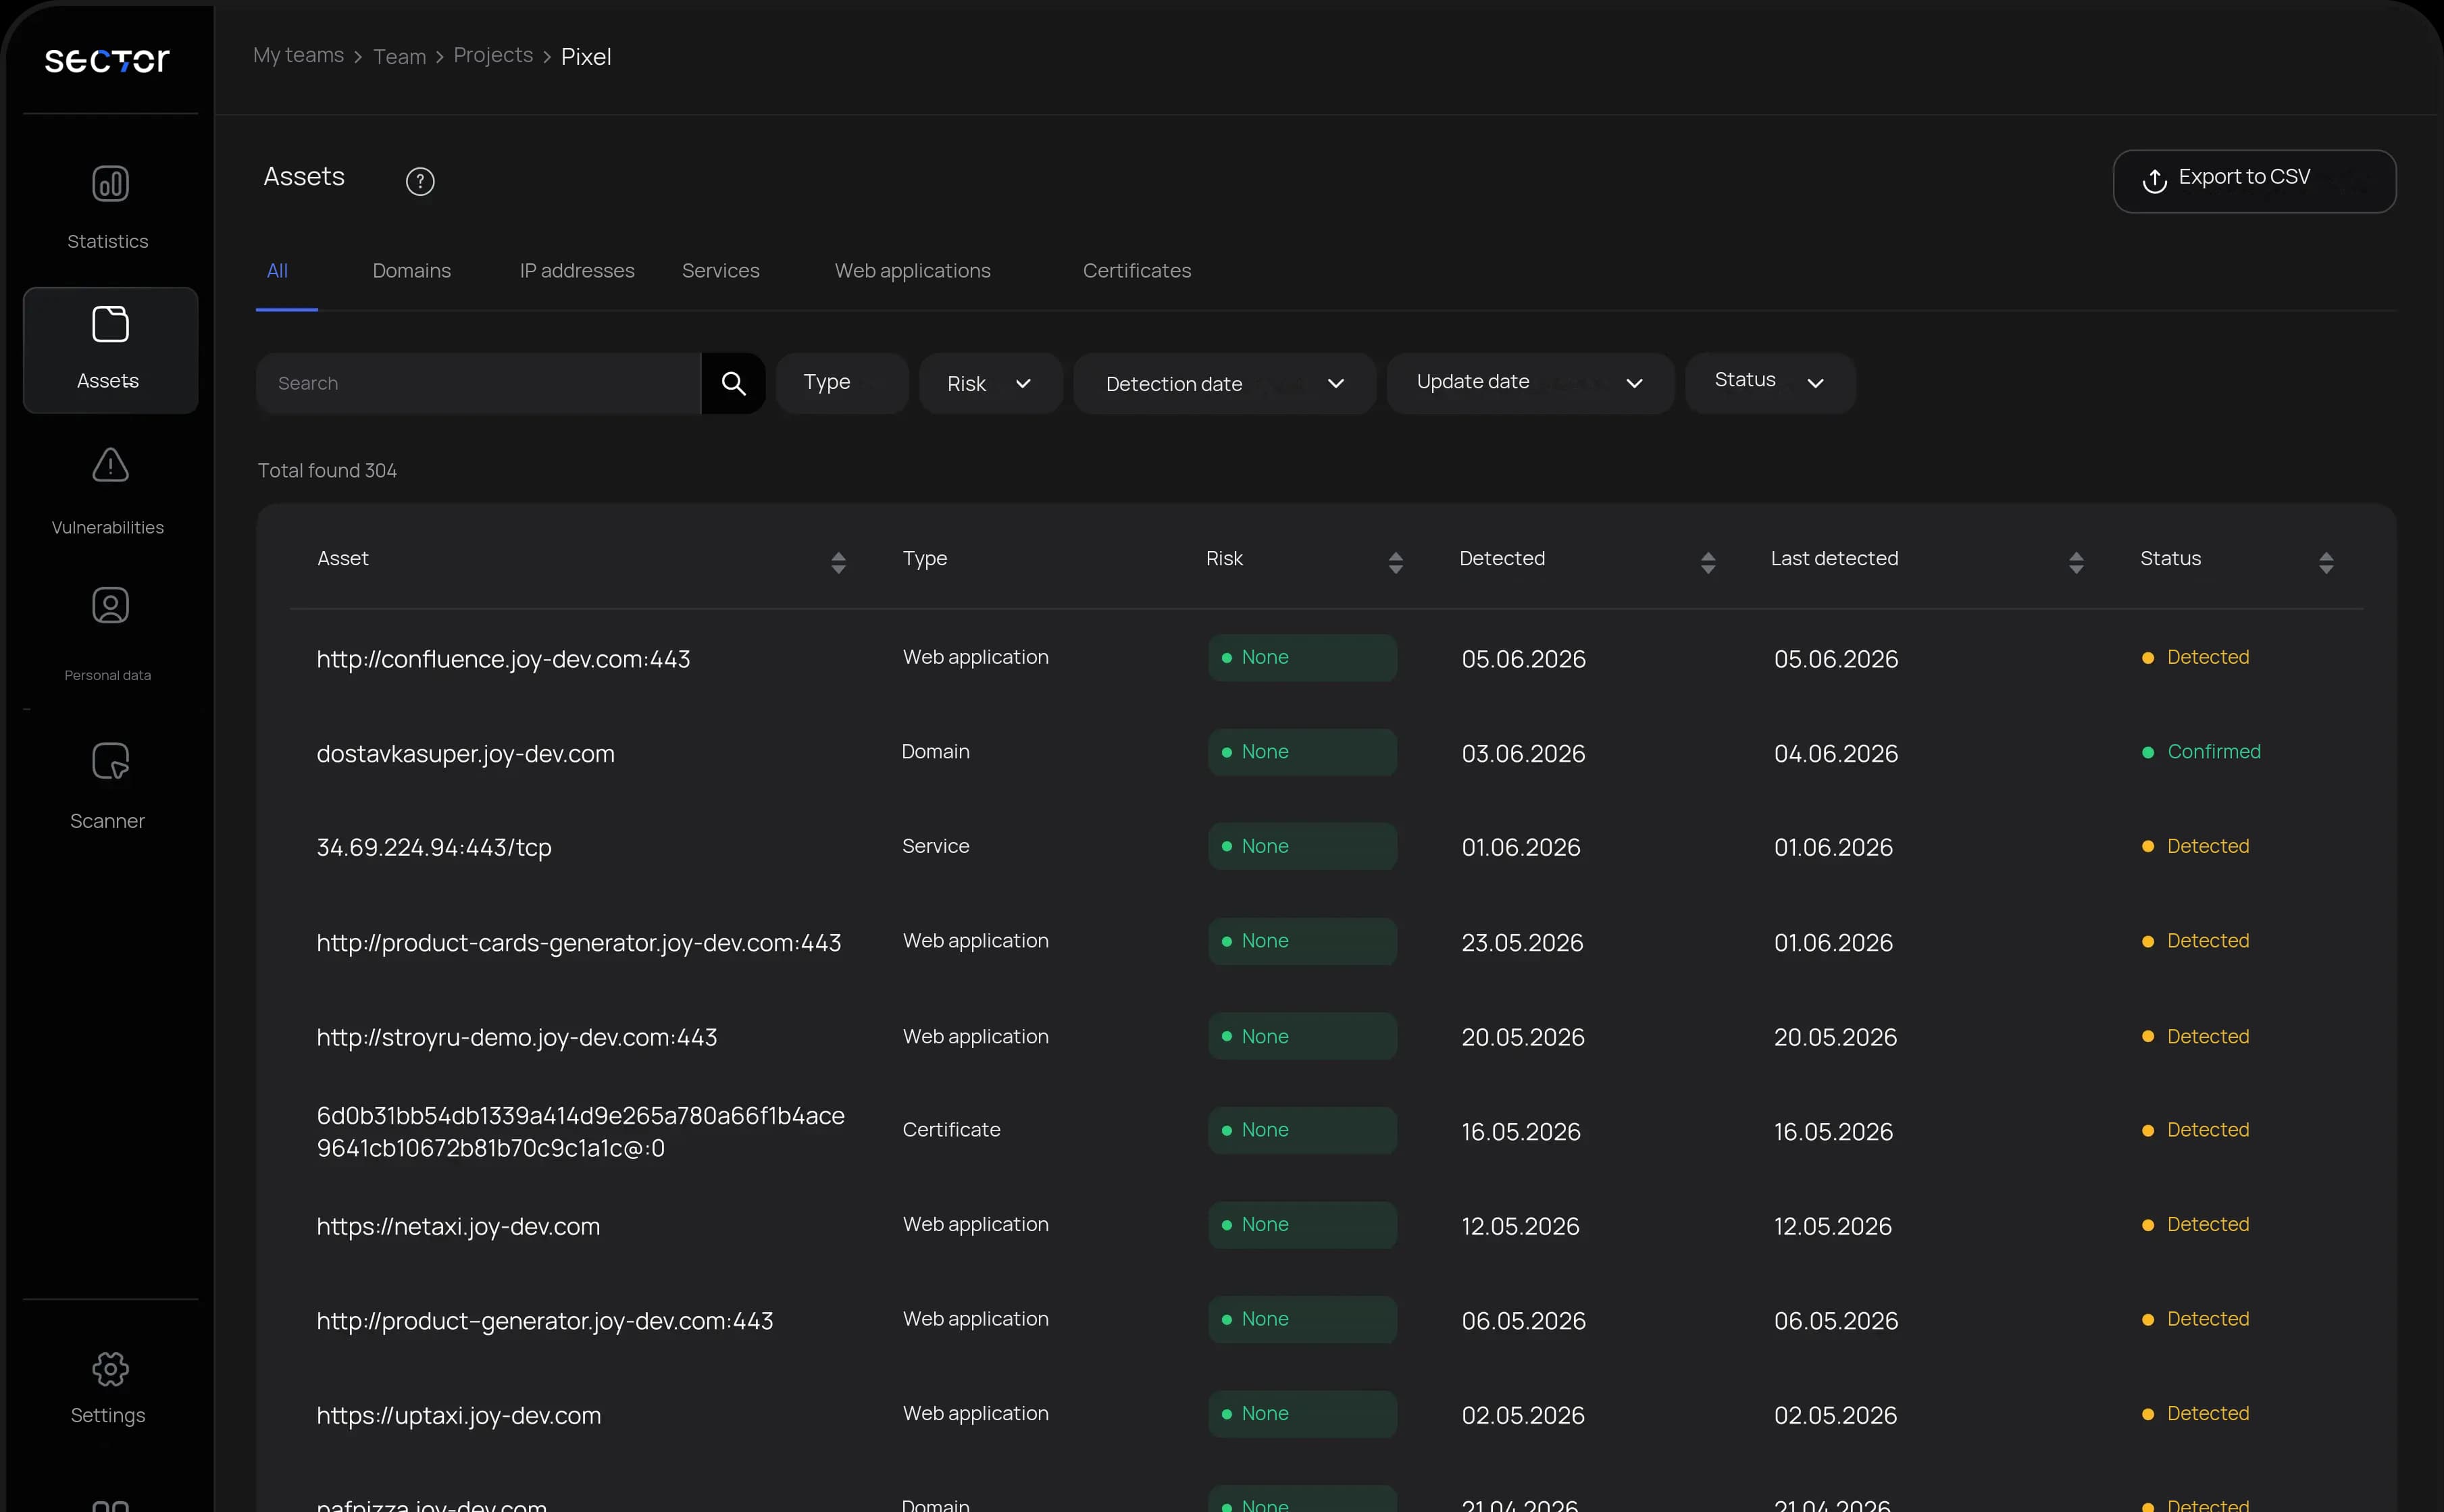
Automatically discover forgotten test environments, exposed admin panels, and subdomains. The platform finds assets your IT team has lost track of before attackers do.
Attack Surface Management (ASM)
SECTOR ASM maps your attack surface and continuously monitors external IT assets. Deployed on premises in your organization’s infrastructure.
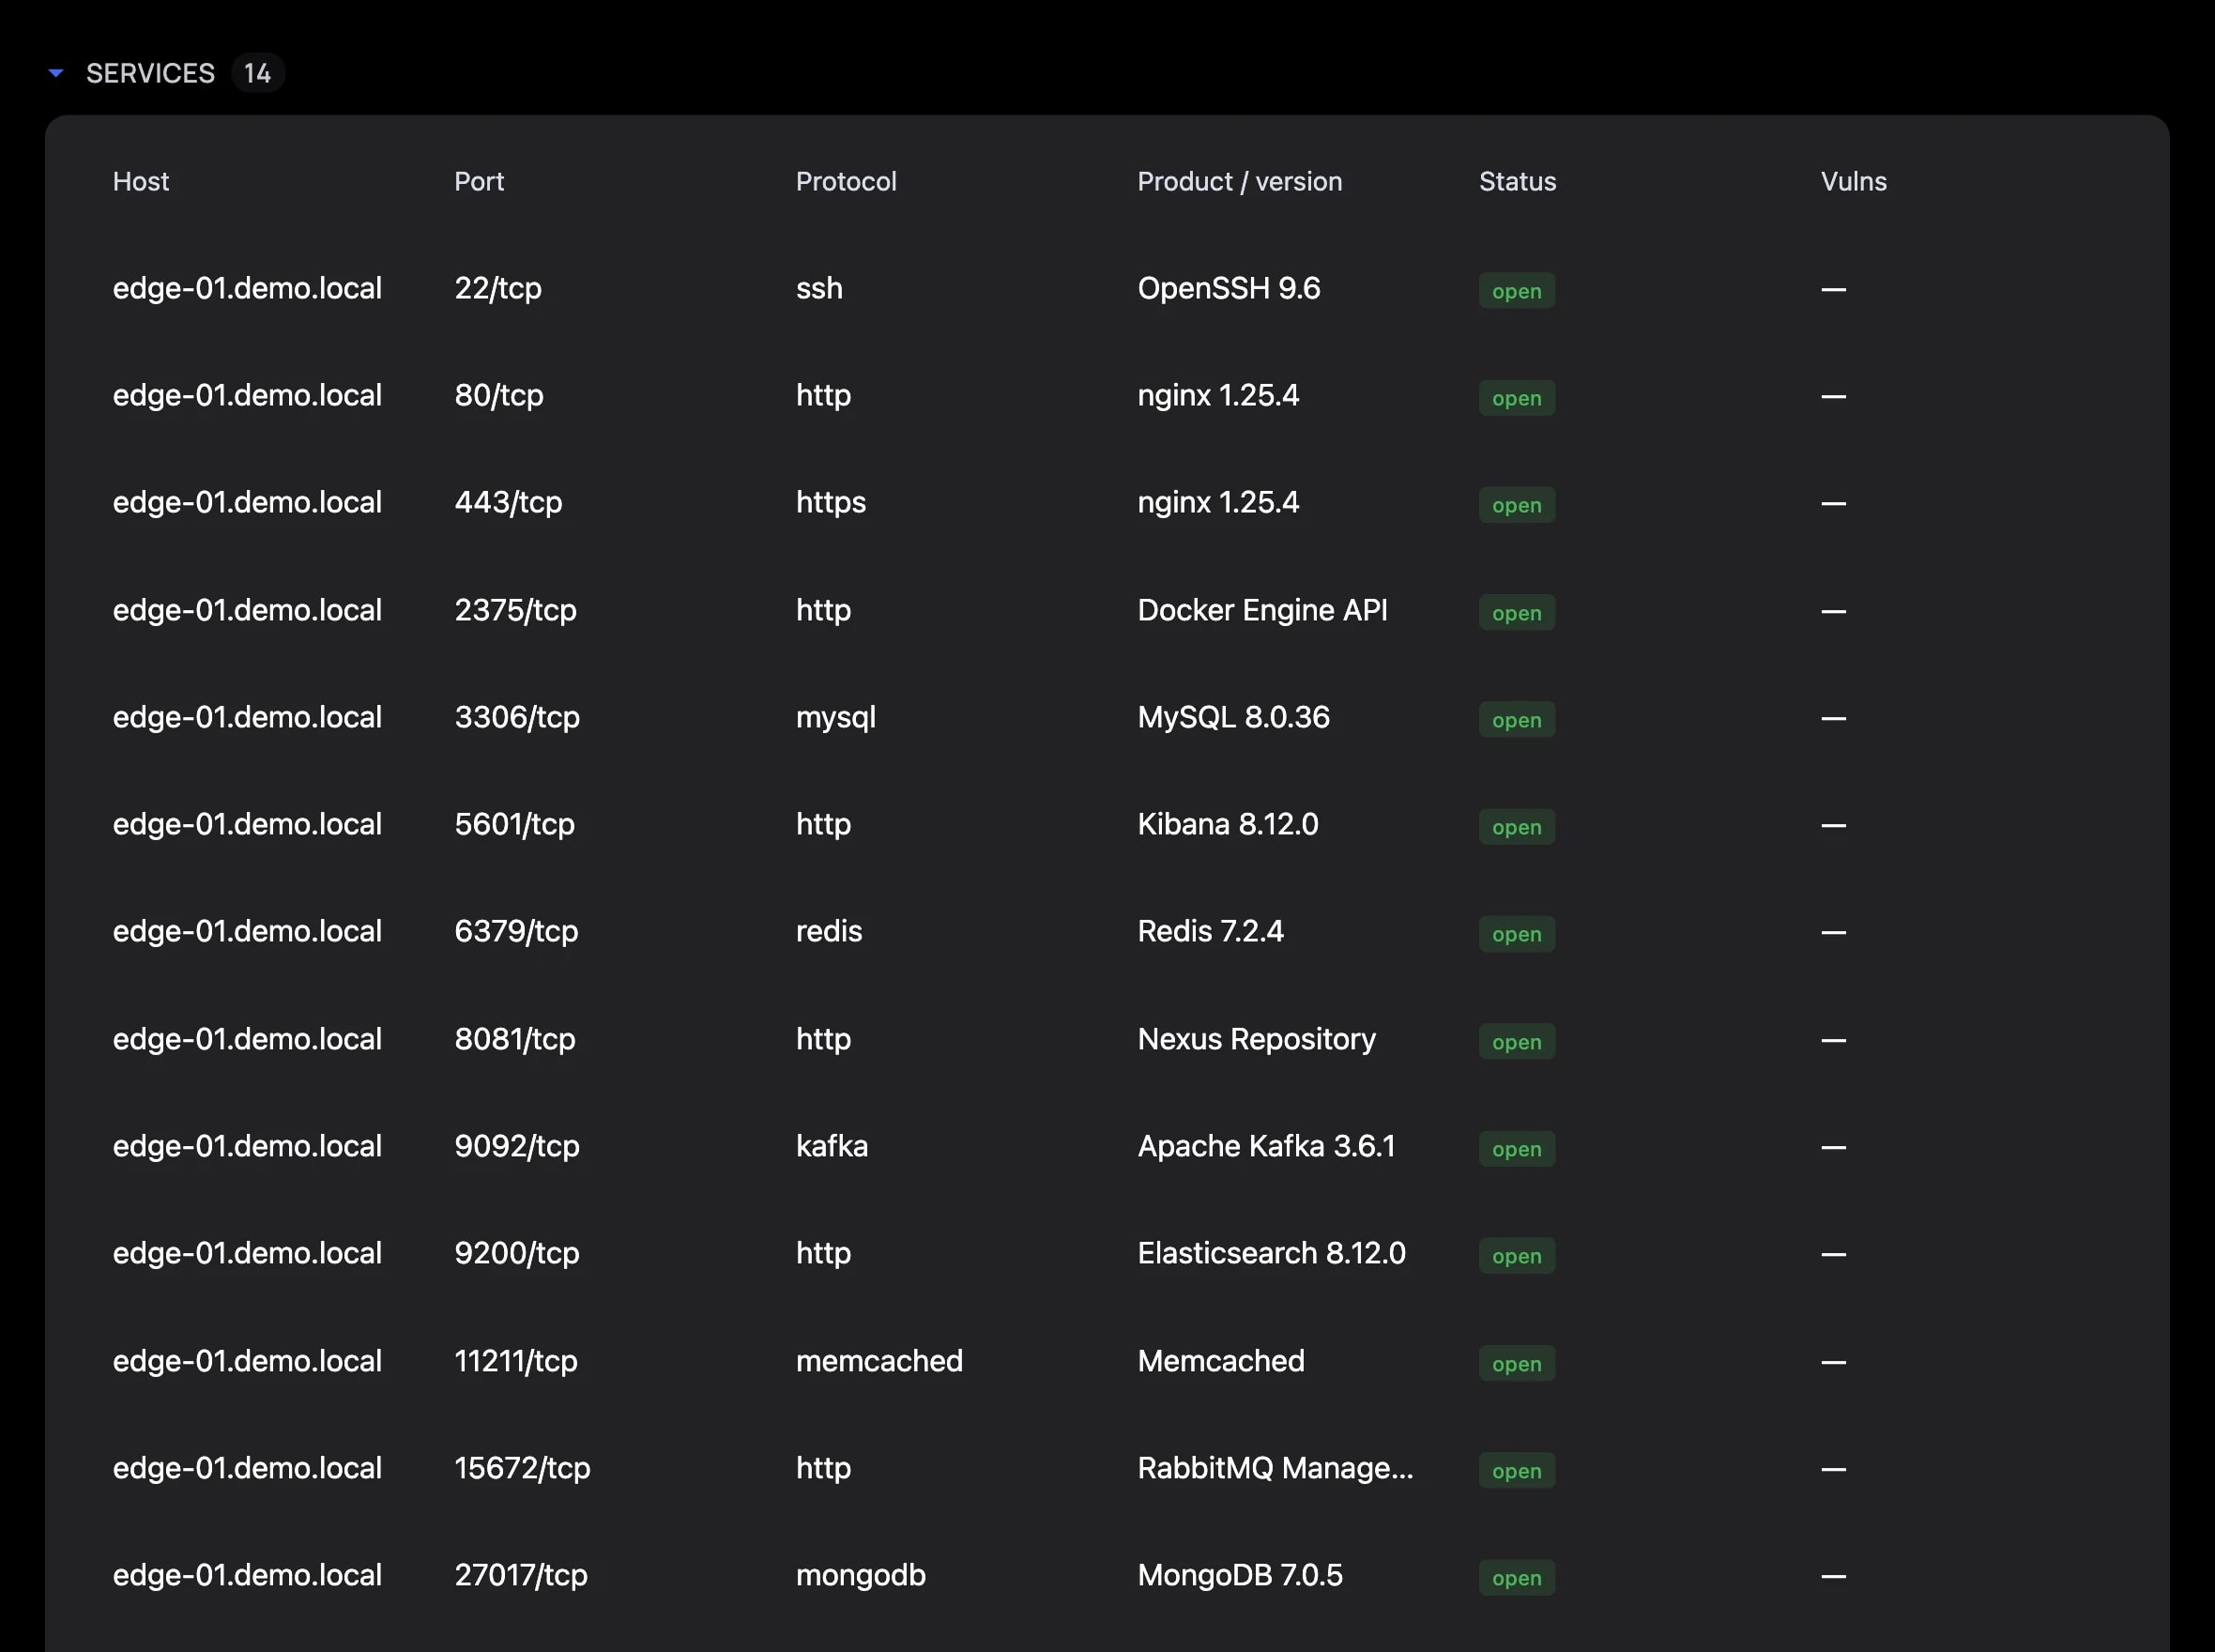
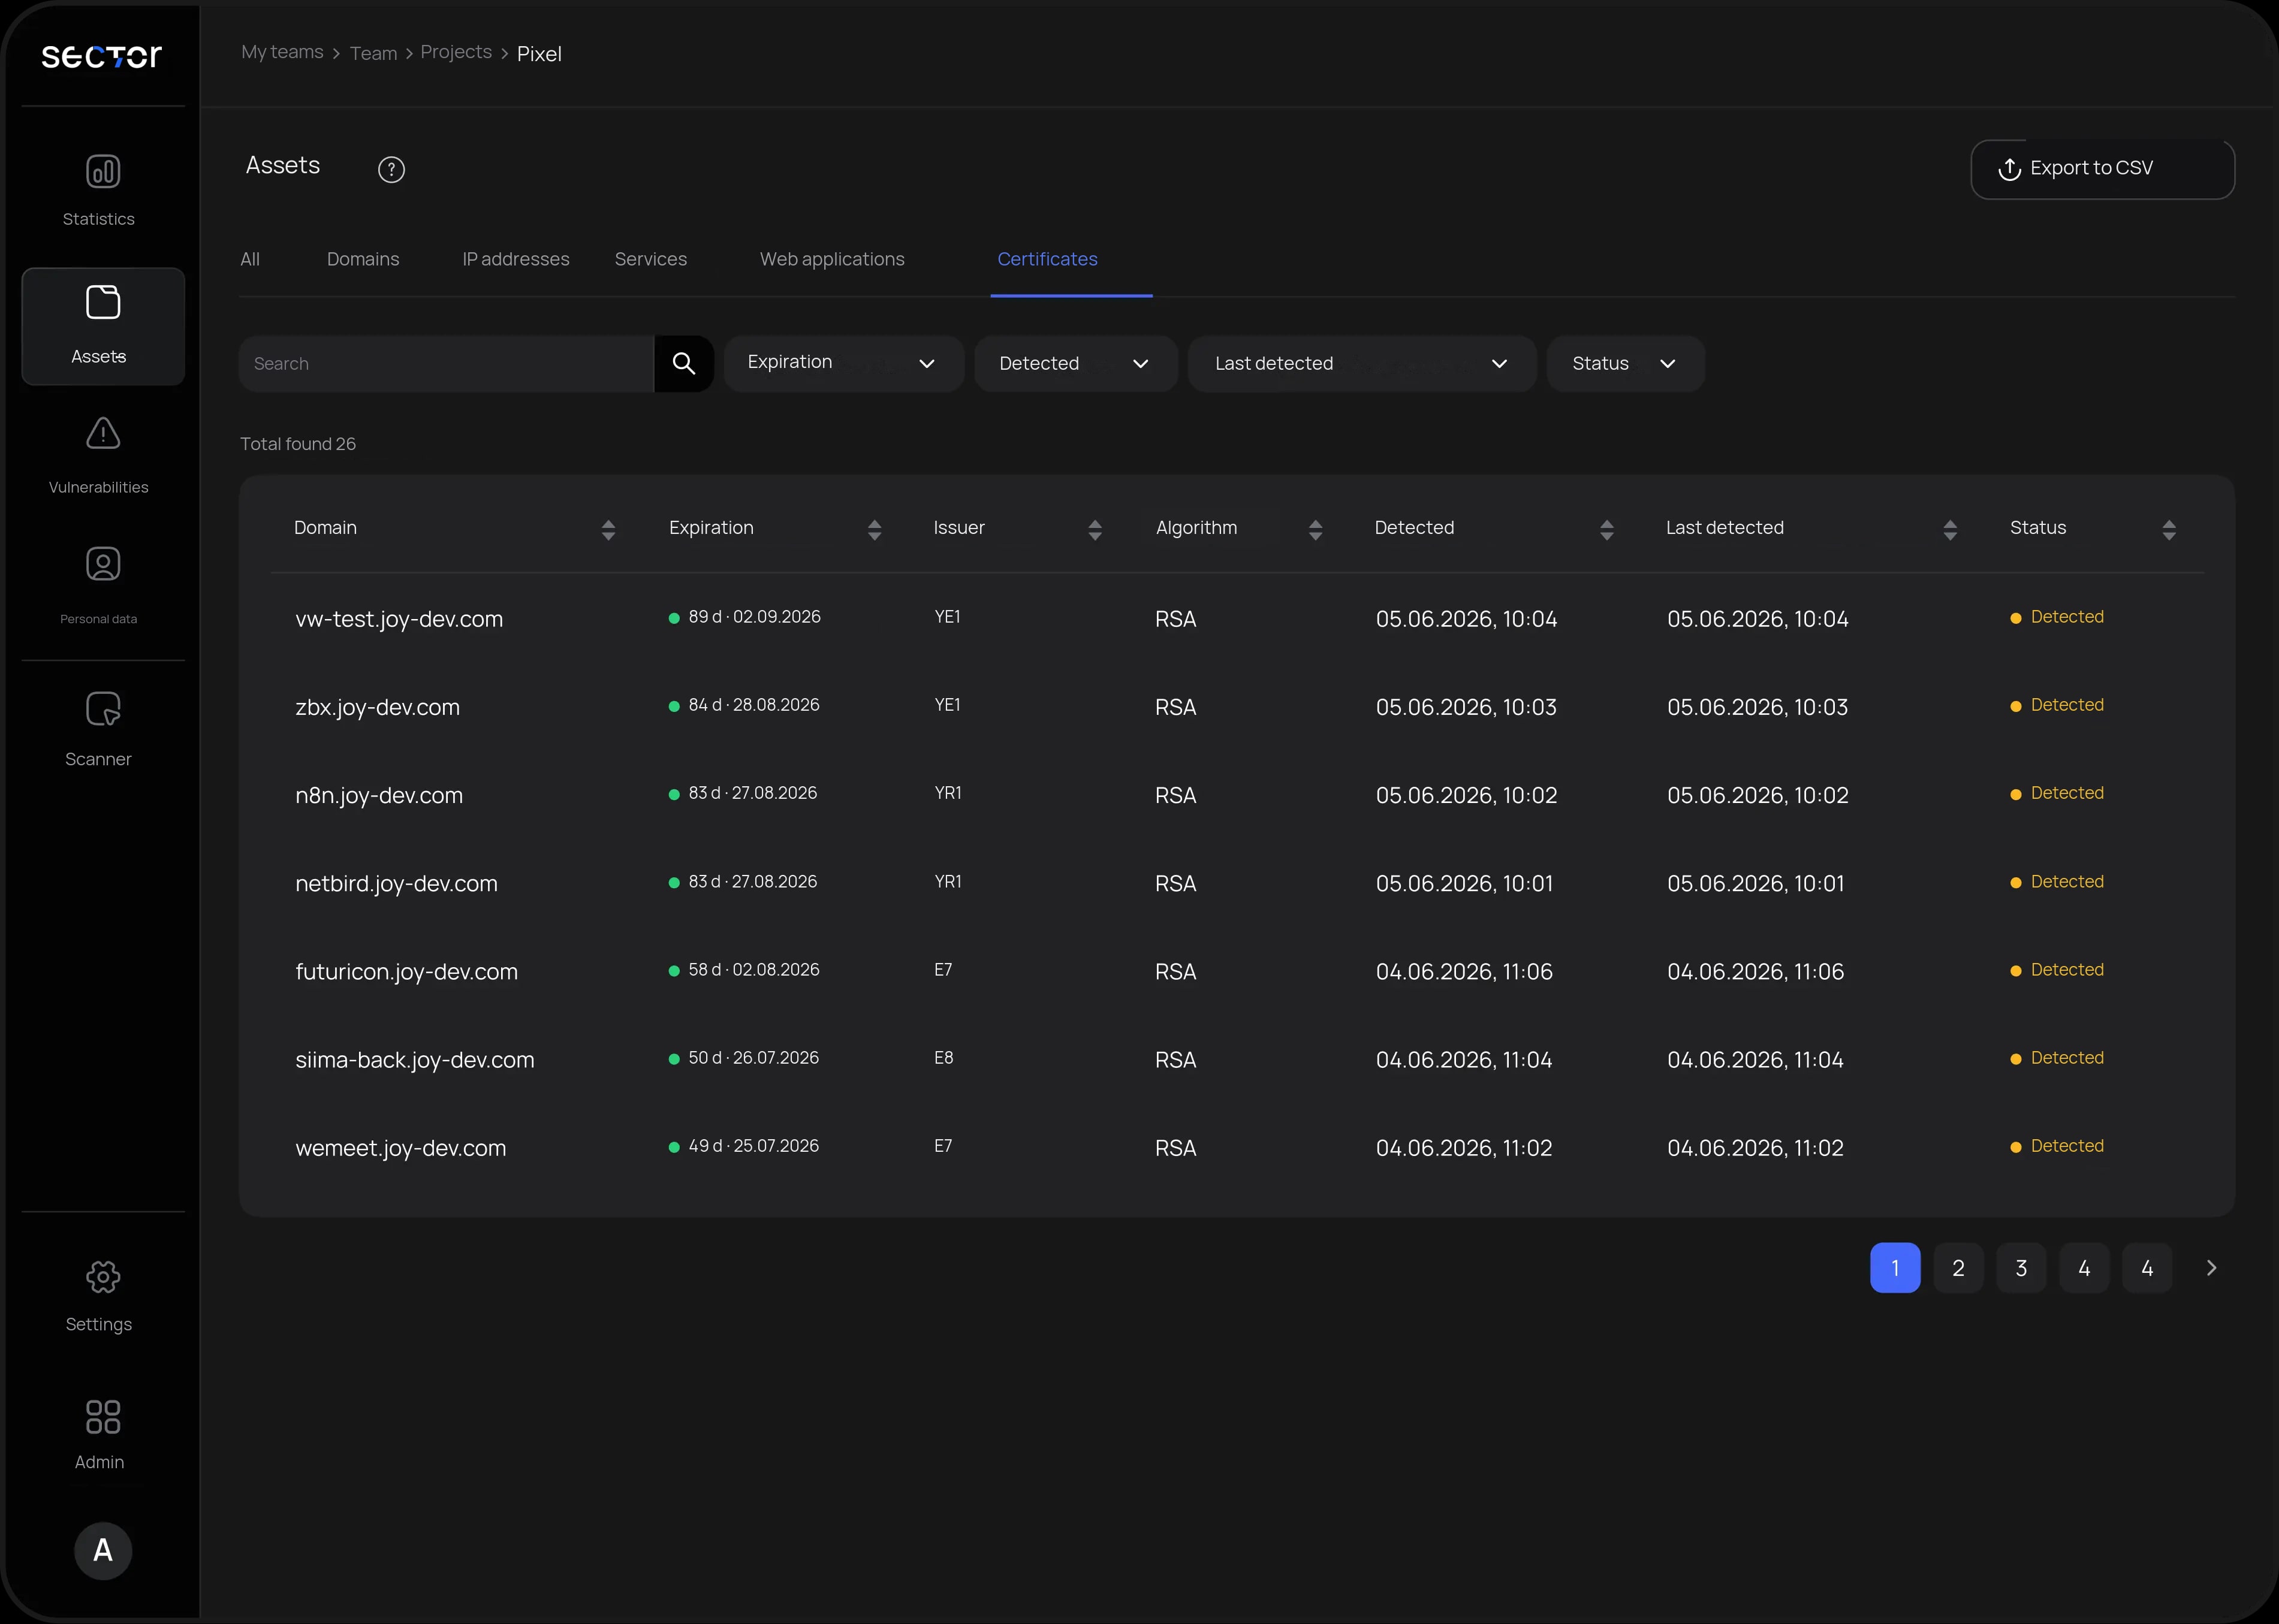
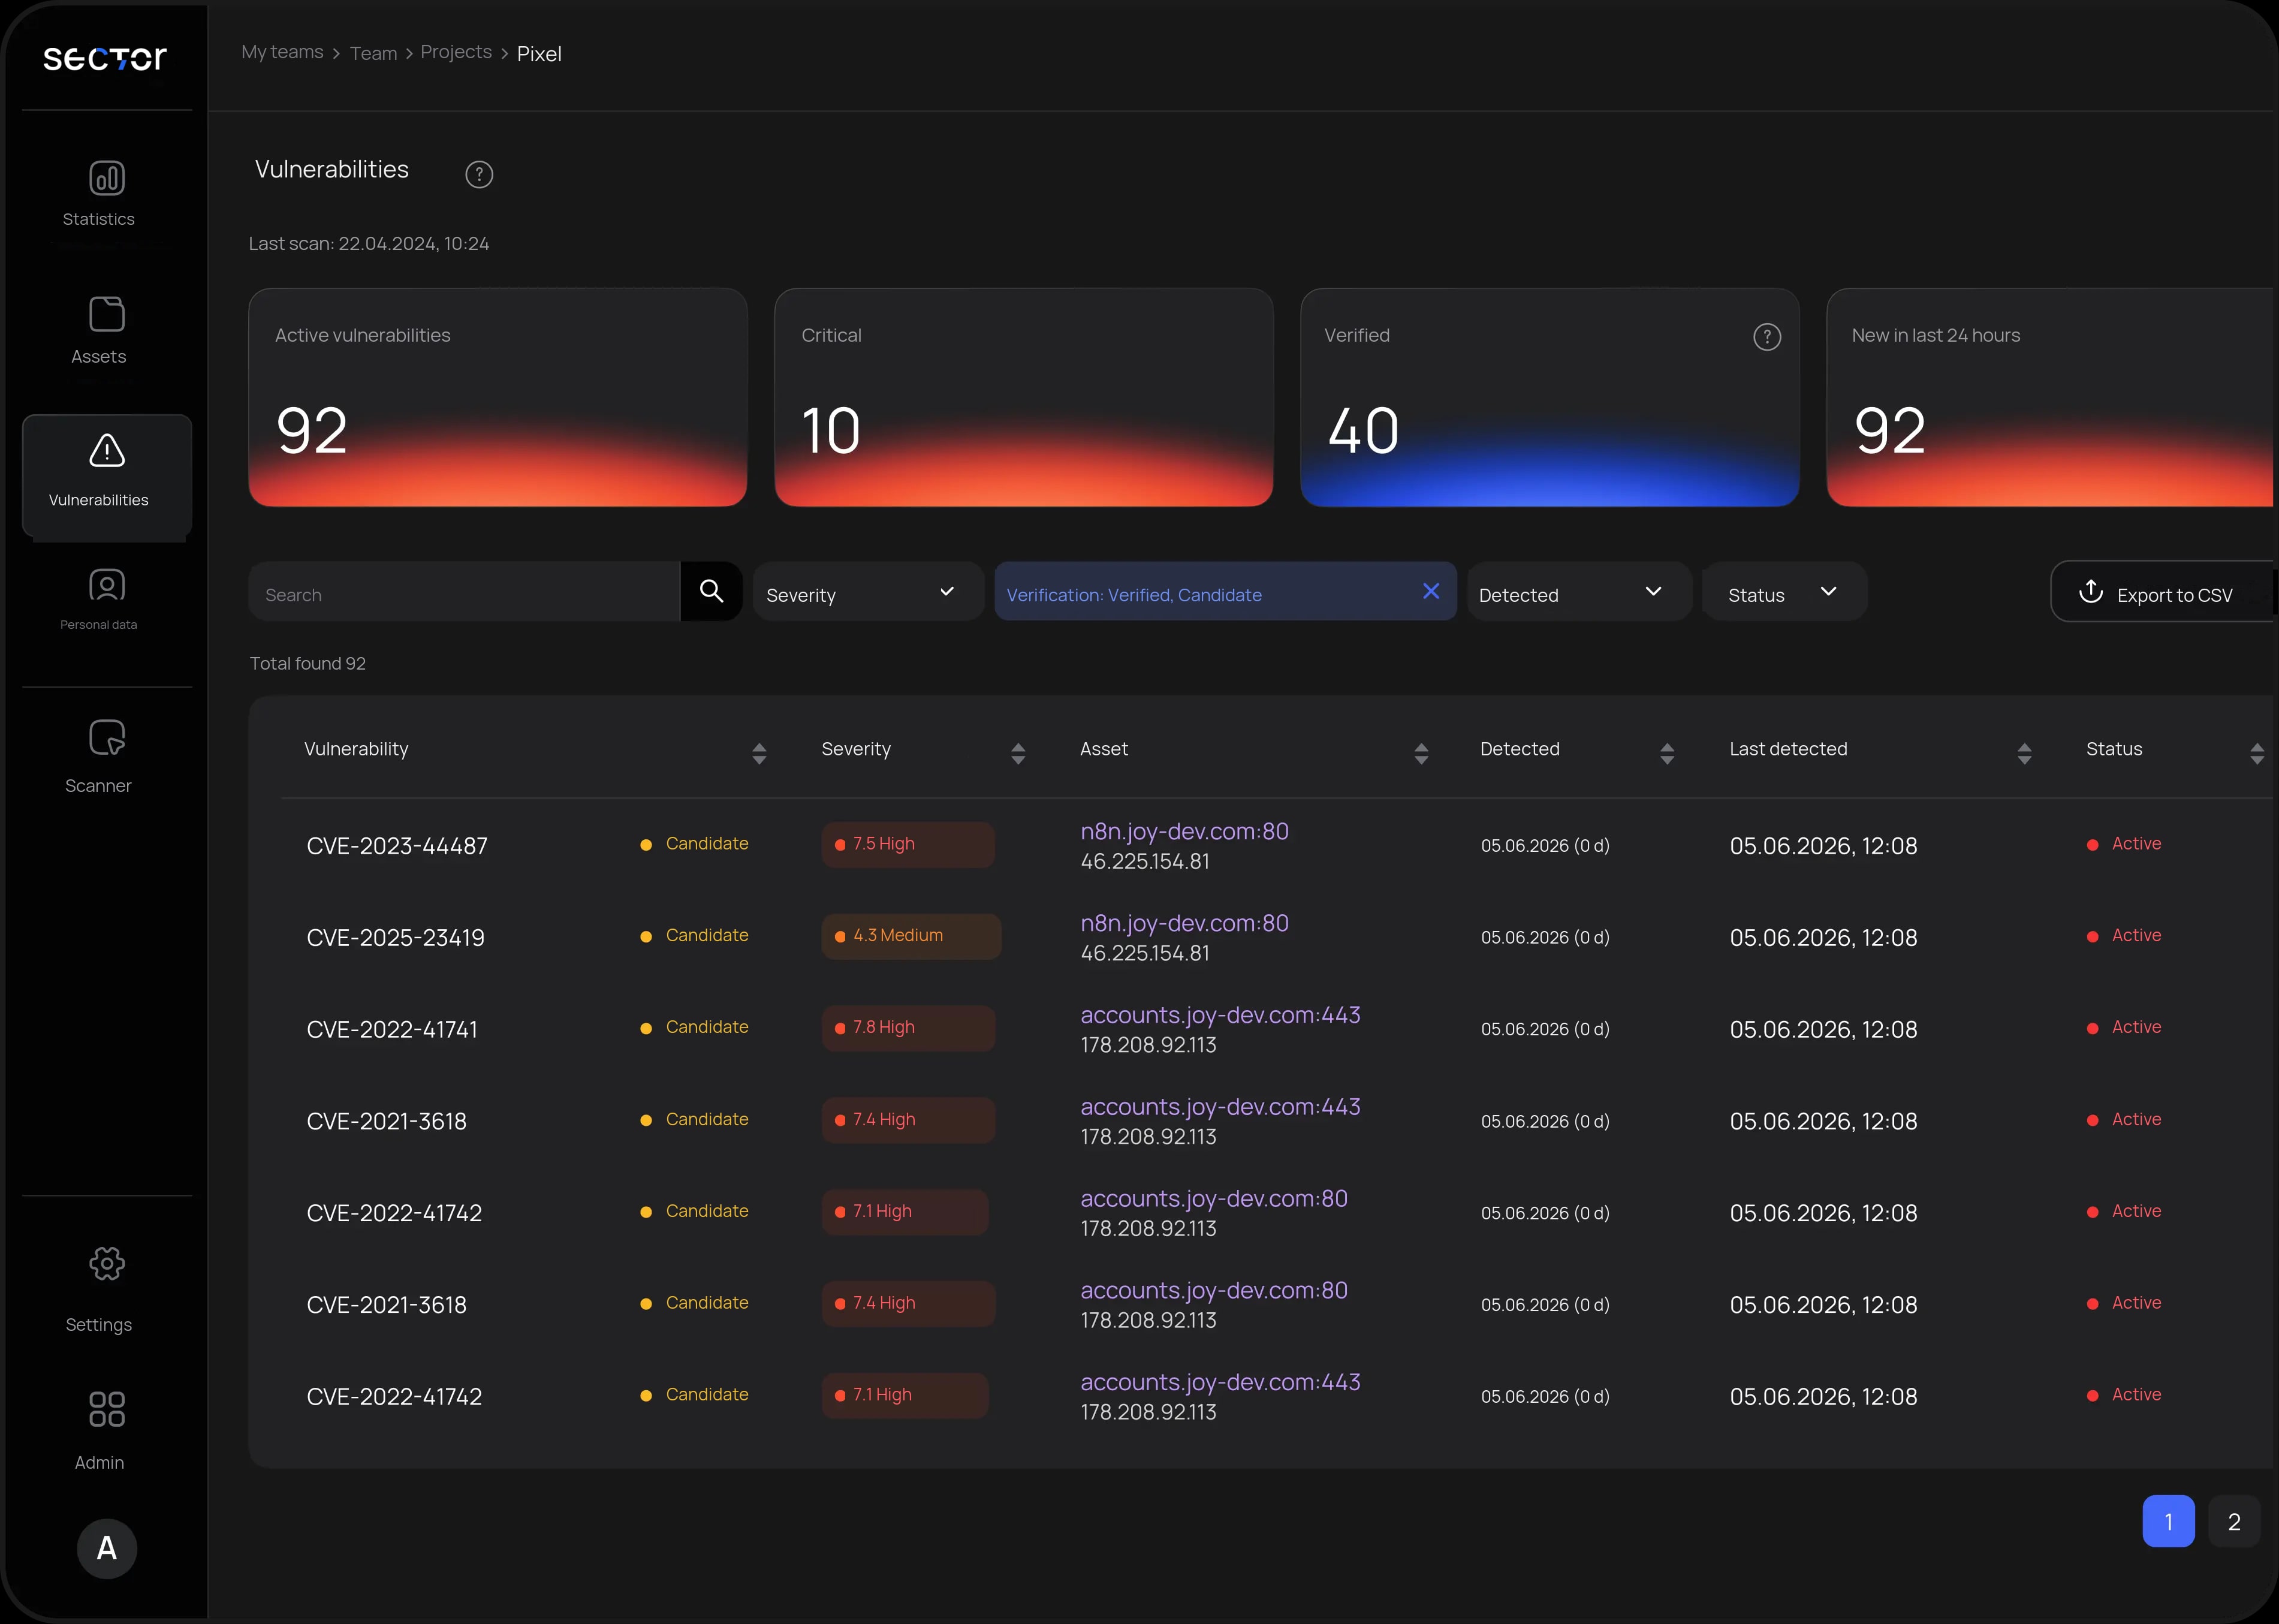
When a critical vulnerability emerges, SECTOR ASM helps identify affected external assets. The system matches vulnerability data against your current service inventory and shows confirmed findings separately. CVSS, EPSS, and exploitation data help security teams prioritize remediation.
The parent organization gains a unified system for automated oversight across every subsidiary. SECTOR ASM regularly scans each branch's external resources using active or passive methods. A scanning node needs no root privileges, so capacity grows by adding nodes, and a perimeter of any size is split between them without gaps. All results are consolidated into a single management report.
Continuously monitor external cryptography, including TLS versions, outdated encryption algorithms, certificate validity, and chains of trust. Vulnerabilities are matched against the FSTEC threat database: a finding carries its BDU identifier, a Russian-language description, and remediation measures, and the affected product shows its Russian Software Registry numbers. Use the results to prepare for FSTEC audits, Federal Law No. 187-FZ requirements, and Bank of Russia regulations.
Leave your name and phone number. We will show how SECTOR ASM automates external perimeter monitoring and SECTOR DRP tracks digital risks.